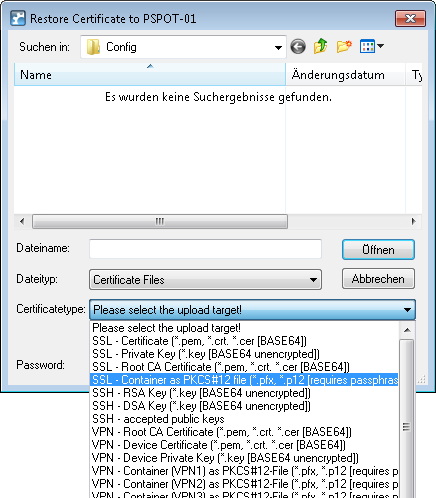
SSL certificate chains can be loaded into the device as a PKCS#12 container. These certificate chains can be used for Public Spot authentication pages by using the HTTPS server implemented in the device. Certificates from recognized trust centers are normally multi-level. Officially signed certificates in the Public Spot are necessary to avoid certificate-related error messages from the browser when authenticating at a Public Spot.
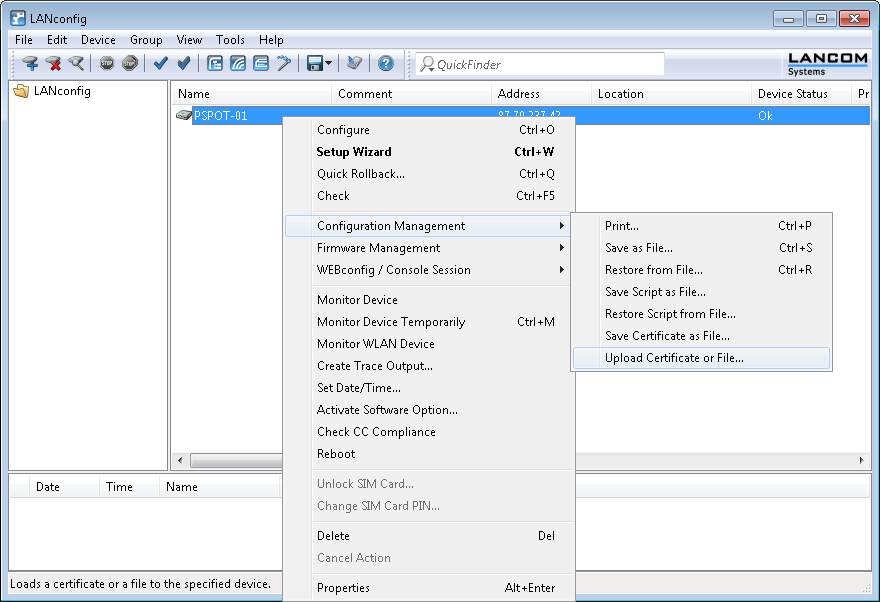
The certificate is loaded into the device for using LANconfig in File Management to upload the individual files of the root CA certificate or a PKCS#12 container:
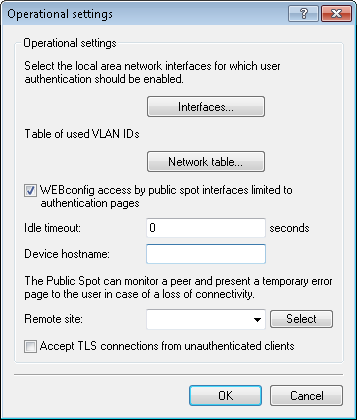
Certificates are normally issued for DNS names, so the Public Spot must specify the certificate's DNS name as the destination and not an internal IP address (enter in under Device hostname). This name has to be resolved by the DNS server to provide the corresponding IP address of the Public Spot.